Use-Case Assessment
Determine whether a proof system solves the requirement better than a simpler design.

ZK technology development for proof systems, selective disclosure and verifiable workflows, with careful circuit design and integration testing.
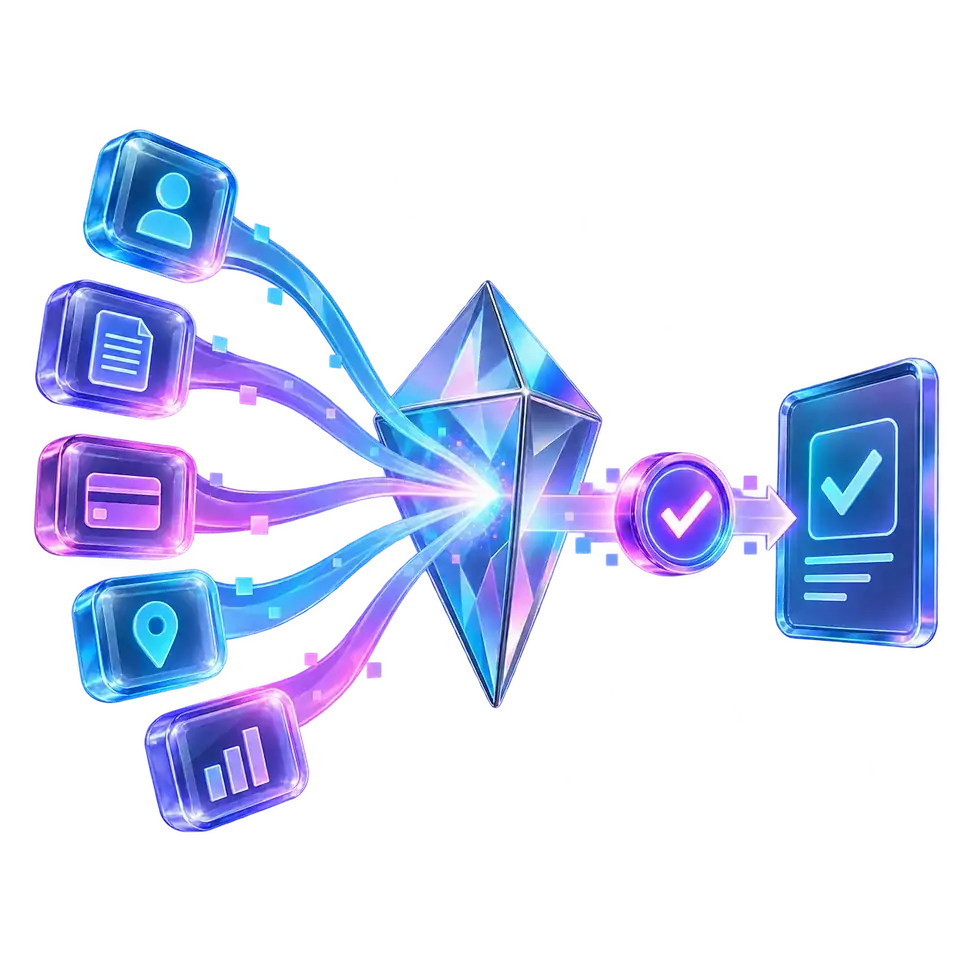
A clear boundary between what is supplied, proved and disclosed.
Inputs intended to remain undisclosed
The claim and permitted public inputs
Compute a proof under the chosen system
Accept or reject the specified claim
Determine whether a proof system solves the requirement better than a simpler design.
Define public inputs, private witnesses and the exact claim a verifier should accept.
Implement scoped constraints with tests for invalid and adversarial inputs.
Connect proof generation to the application and its performance requirements.
Integrate verification with contracts or backend services as appropriate.
Measure proving costs and prepare implementation evidence for specialist review.
We choose the implementation tools after confirming the architecture and integrations.
Write the statement, threat model and disclosure requirements.
Evaluate proof frameworks and prototype the critical constraints.
Implement circuits and application proving/verification interfaces.
Test invalid witnesses, disclosure risks and practical performance.
Deliver reviewed artifacts and operational guidance for the agreed scope.
Using a ZK-related framework does not automatically make an application private. Public inputs, metadata, proving infrastructure and surrounding application behavior can still reveal information.
What exact fact does acceptance establish?
Which data is public and which must remain private?
What setup, operator or hardware assumptions exist?
Can the application support the proving and verification workload?
Prove an approved attribute without disclosing the whole record.
Check a defined computation through a supported proof system.
Verify scoped participation criteria with deliberate privacy boundaries.
Integrate existing proof technologies into useful products.
No. Privacy depends on the statement, public inputs and the surrounding system. Validity proofs alone do not guarantee application privacy.
Specialist cryptographic and circuit review may be required in addition to application security testing.
Some workloads can. Feasibility depends on the proof system, input size, device limits and user-experience requirements.
Tell us what you want to build. We’ll help define the next practical step.